⚠️ Windows 0-Day Exploited to Deploy Play Ransomware (CVE-2025-29824)
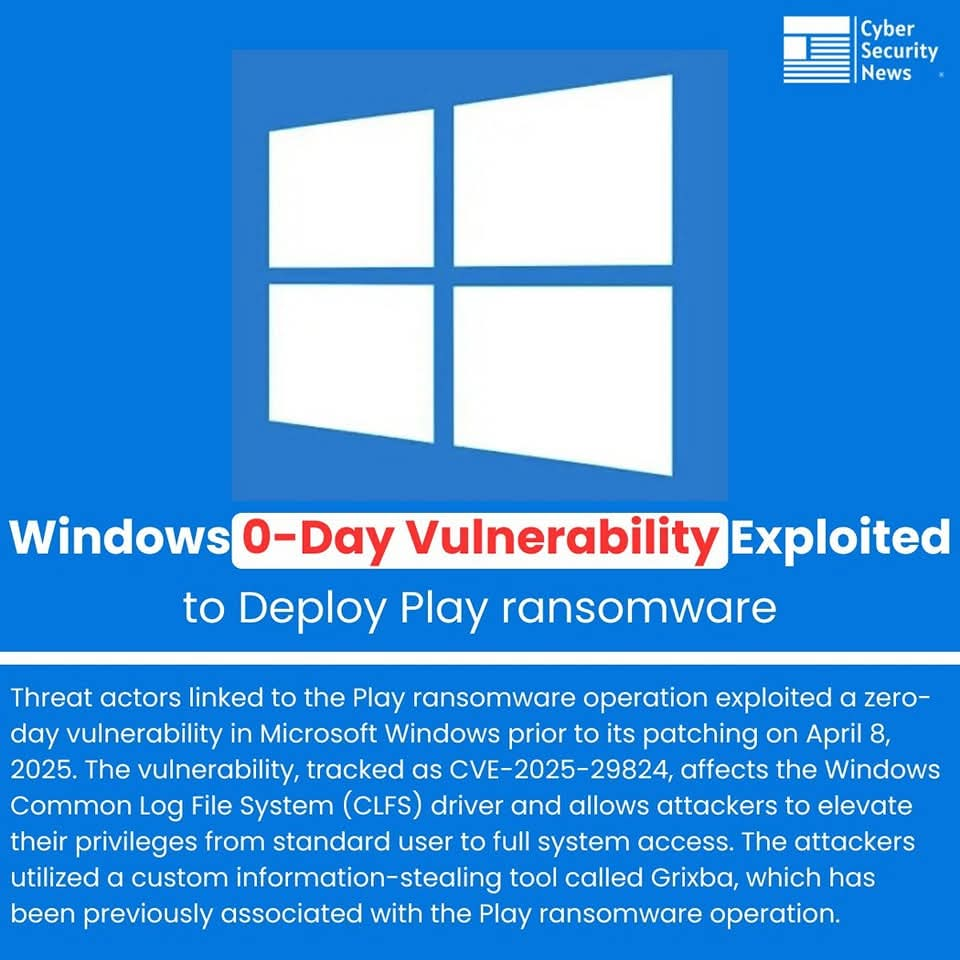
Threat actors associated with the Play ransomware group exploited an unpatched Windows 0-day vulnerability affecting the Common Log File System (CLFS) driver.Tracked as CVE-2025-29824, the flaw enabled privilege escalation from standard user to full system access — before being patched on April 8, 2025.The attackers also used a custom info-stealer named Grixba, previously linked to Play ransomware campaigns.Disclaimer: This content is shared solely for educational and awareness purposes. It does not promote or support exploitation or unauthorized access.#WindowsZeroDay #CVE202529824 #PlayRansomware #CyberSecurity #InfoSec #CLFS #EducationOnly #PrivilegeEscalation #PatchNow #ThreatIntel
Views: 0